Bluemark for Odoo
GDPR
Personal data, governed — not merely declared.
GDPR adds the compliance layer on top of the document register: processing purposes, consents and their expiry, data subject requests, legal hold on a document and controlled destruction, with an access log and a destruction log.
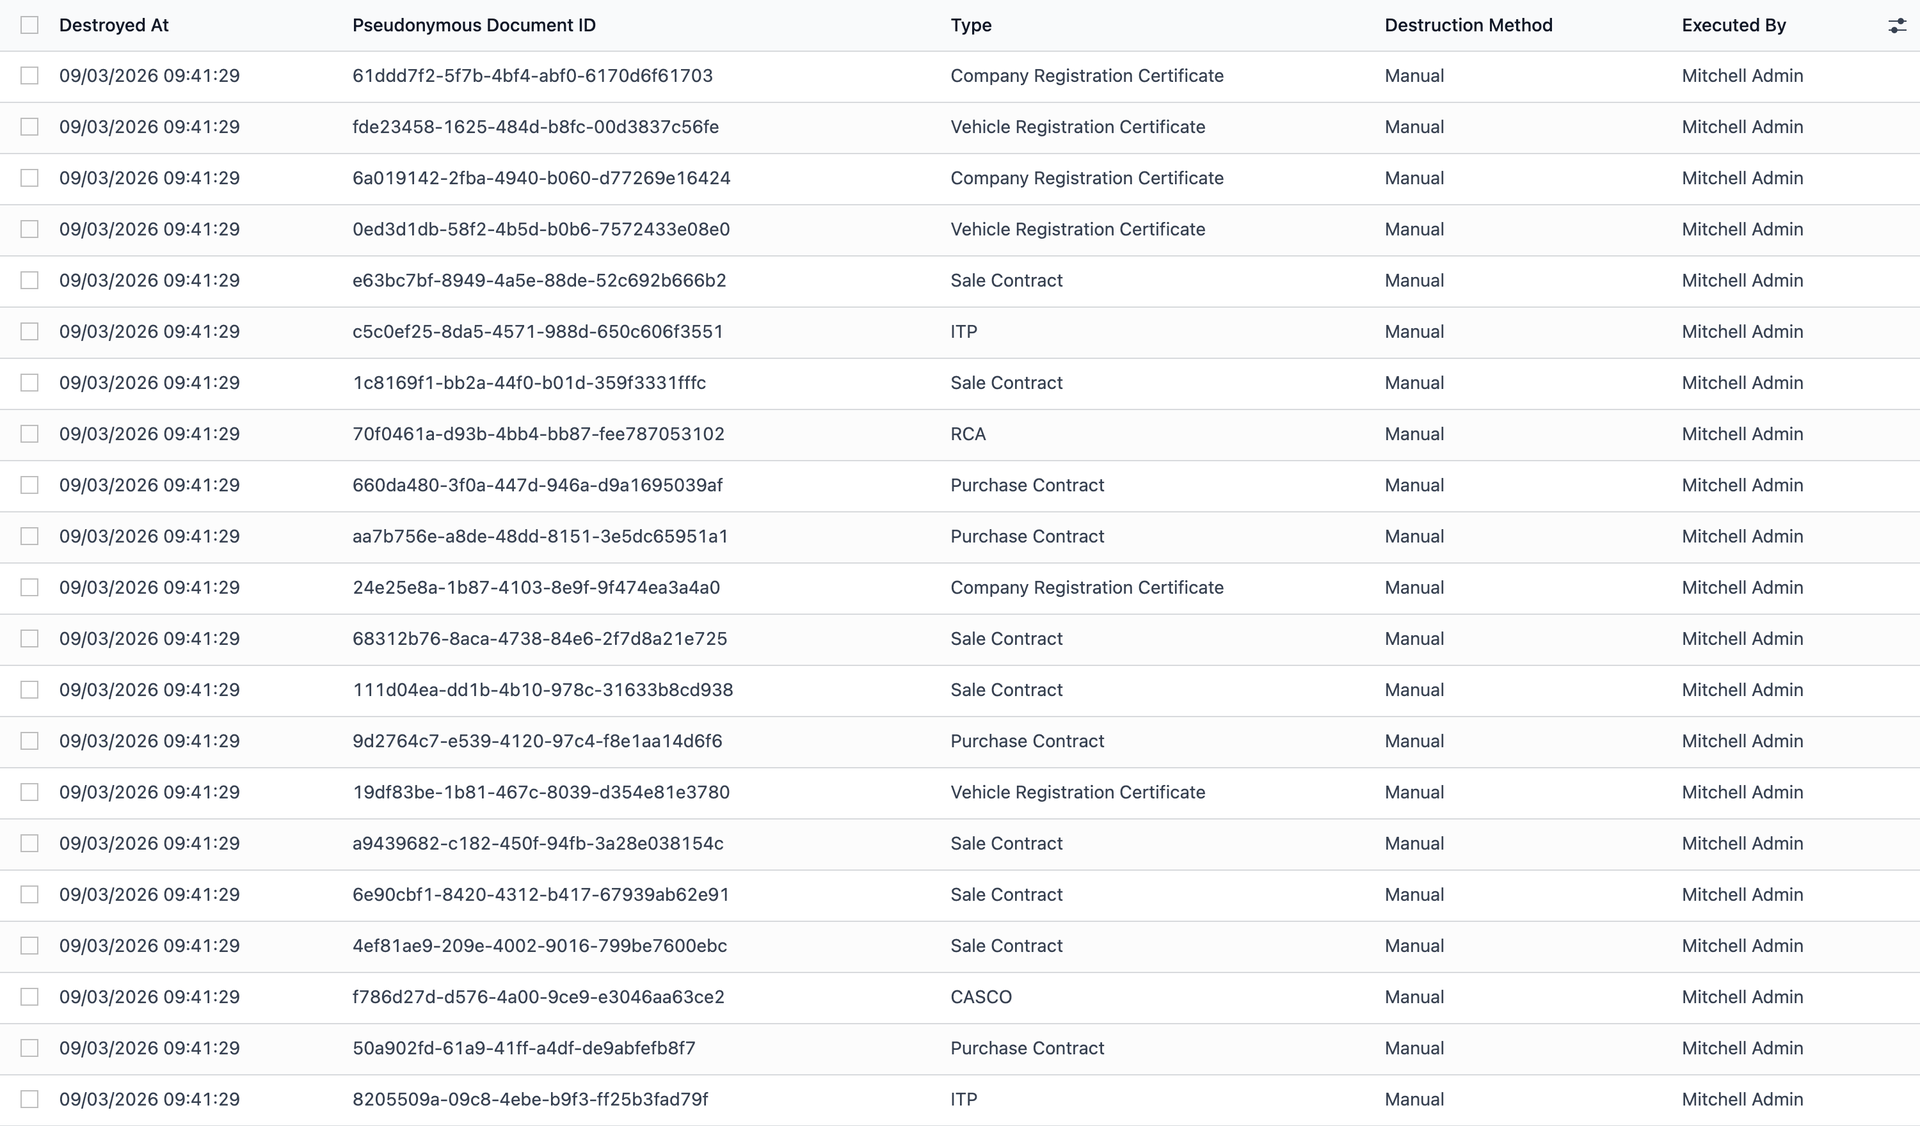
The destruction log
Every destroyed document survives as evidence: what it was, who approved it, when it was carried out and on what basis. The file goes; its trace stays.
What you get
Processing purposes
The lawful basis for keeping each data category, applied to document types.
Consents with an expiry date
Tracked automatically instead of being remembered by someone.
Data subject requests
Access, rectification, erasure — logged, numbered and carried to the end.
Legal hold
A document under litigation cannot be destroyed, and the reason is required.
Destruction you can prove
What was destroyed, who approved it and when — even after the file is gone.
Access log
Who opened a document holding personal data, and when.
Questions it answers
- On what lawful basis do we keep each category of personal data?
- Which consents do we hold, and which have expired?
- What data subject requests did we receive, and where do they stand?
- Which documents must not be destroyed because they are under litigation?
- In an inspection, can we prove what we destroyed and who approved it?
GDPR is implemented by Odoo partners.
Tell us what you need and we will point you to one — or talk to the partner you already work with.